OUR BLOGS
News and Insight from our expert team.
Explore practical insights, strategies, and ideas for modern forensic investigations.
Search blogs by title
Showing 19 results out of 19.
Expert Witness AI Audits: Spotting Unvetted GenAI in Court
Uncover unvetted GenAI in expert reports. Learn how expert witness AI audits expose hallucinated data, prompt flaws, and evidentiary vulnerabilities.
DOJ Directive 26-12: Updating Corporate Fraud Protocols
Examine DOJ Directive 26-12 issued on Oct 1, 2026. Learn how to update corporate fraud protocols and alignment with new enforcement priorities.
SIEM Logs Employee Fraud Evidence: The Legal Myth | FICS
Relying on SIEM logs alone to prove employee fraud in court fails. Discover why SIEM event streams lack digital forensics admissibility and how to build real legal proof.
Memory Imaging vs Network Logs: Catching Tampered Records
Learn how memory imaging catches tampered records that network logs miss. Discover SANS DFIR benchmarks and an actionable IR decision framework.
How to Audit Vendor Supply Chains for Hidden Ownership Risks
Learn practical, forensic steps to audit vendor supply chains for hidden ownership risks and identify foreign shell companies before compliance failures hit.
Synthetic Identity Fraud: Defending Onboarding Against Deepfakes
Examine how deepfakes and synthetic identity fraud compromise enterprise onboarding, and discover forensic strategies to secure verification workflows.
Mobile IR: Logical iTunes Backups vs Physical Forensic Imaging
Compare logical iTunes backups against physical forensic imaging for mobile IR. Discover artifact loss risks and a clear decision framework for iOS investigations.
DC3 Warns of WaterPlum IT Attacks: Audit Hiring Vetting
The DC3 advisory warns of WaterPlum IT attacks targeting hiring pipelines. Learn how to audit hiring vetting processes to stop North Korean cyber actors.
Enterprise GenAI Forensic Sandboxing: Why It Is Essential by 2027
Discover why enterprise GenAI forensic sandboxing will be mandatory by 2027. Learn how immutable logs protect against regulatory and legal risk.
Forensic Logs vs API Tokens: Close Identity Audit Gaps
Close the 33% identity audit gap with our definitive framework comparing API tokens and forensic logs for enterprise compliance and legal evidence.
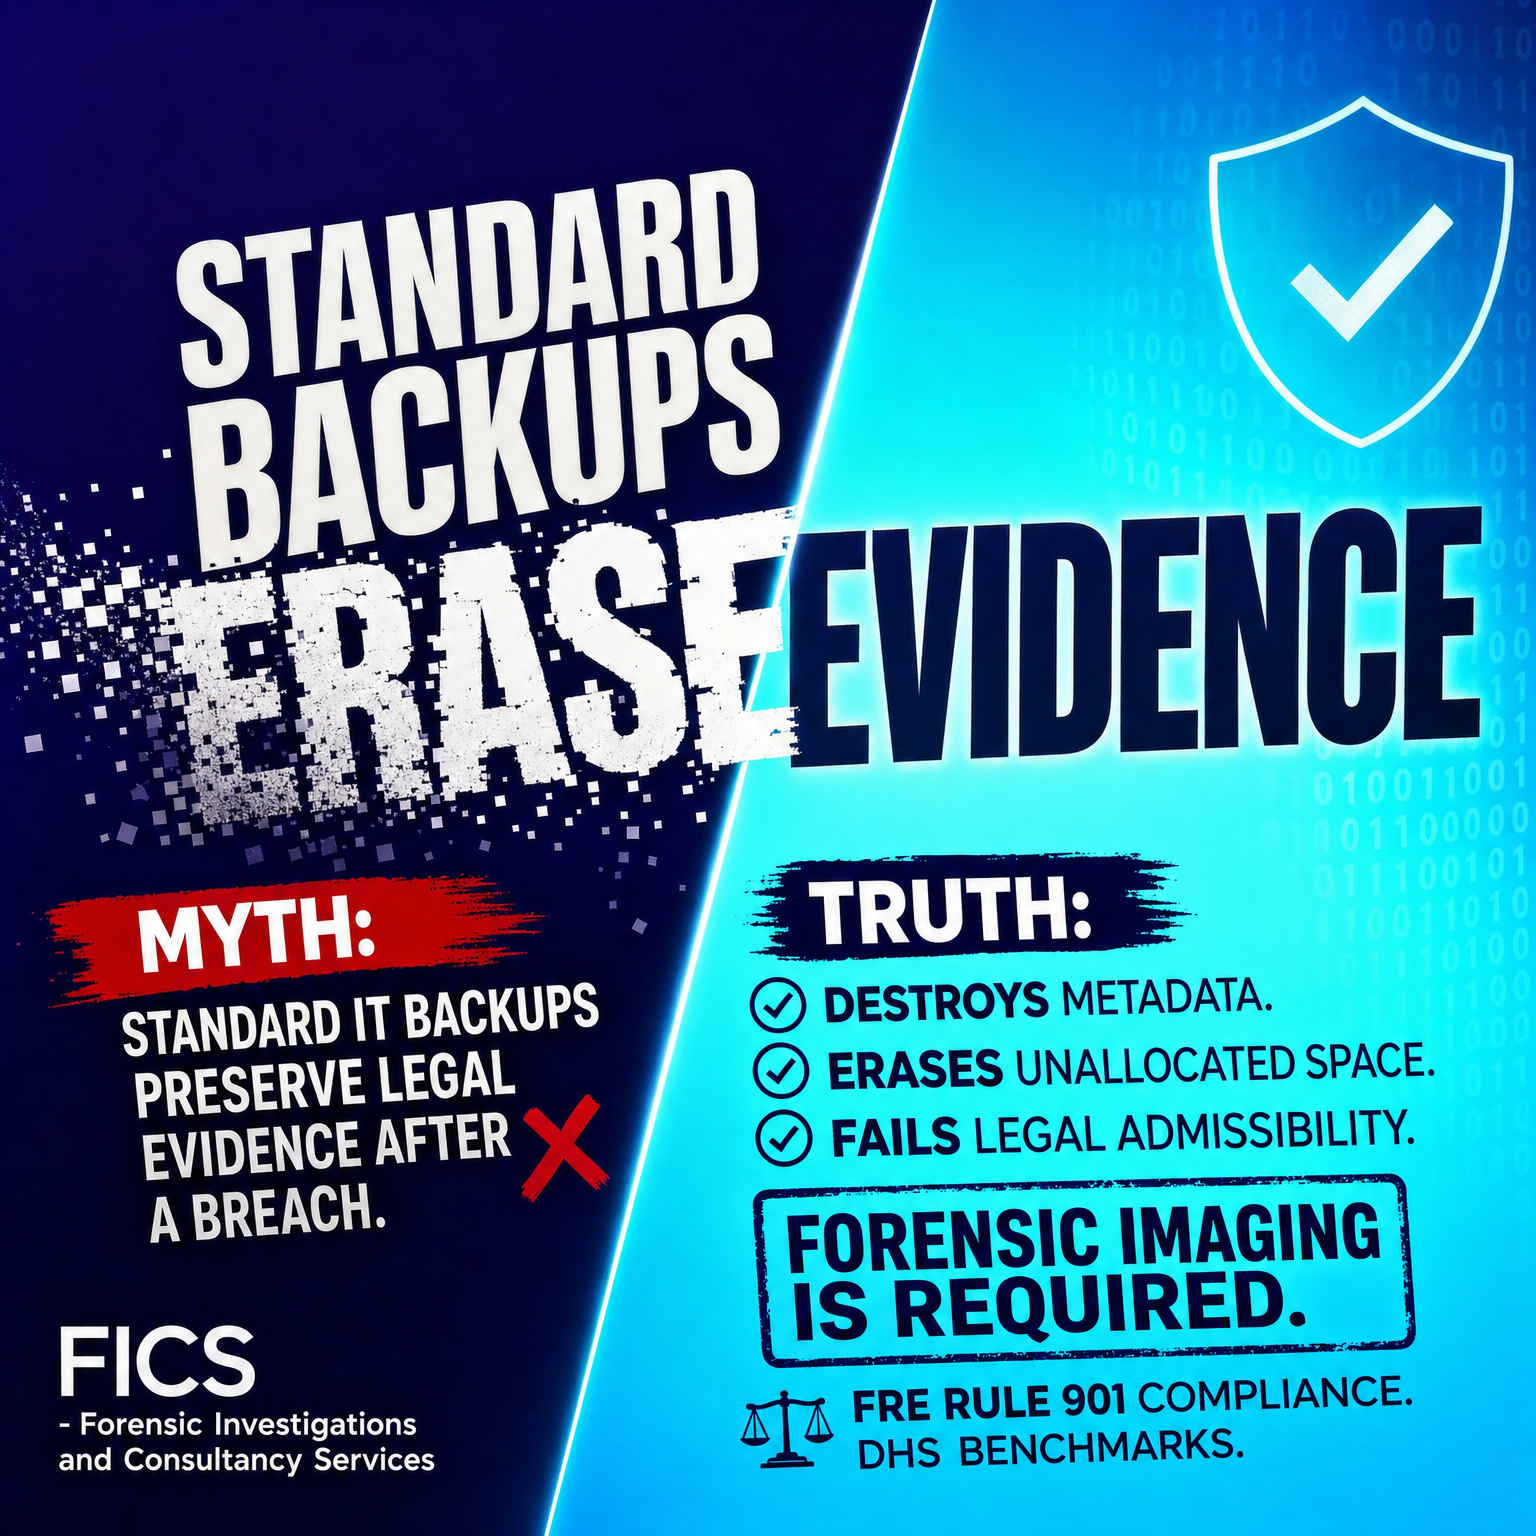
Why IT Backups Fail as Legal Evidence After a Breach | FICS
Standard IT backups destroy metadata and erase unallocated space. Learn why forensic image evidence is required under FRE Rule 901 and DHS benchmarks.
SEC Private Fund Charges: Forensic Asset Tracing Guide
Recent SEC private fund charges highlight the need for forensic asset tracing in fraud schemes. Learn how FICS unravels complex fund misappropriation.
Why Screenshots Fail in Court: Verifying Digital Metadata
Discover why courts reject simple screenshots as digital evidence and learn how verifying digital evidence metadata ensures legal admissibility.
Digital Evidence Handling Gaps: Oxford Study Insights for Counsel
Oxford's study exposes critical digital evidence handling gaps in major investigations. Learn how legal counsel can address operational readiness risks.
Trace BEC Wire Transfers: FBI 72-Hour Kill Chain Guide
Learn how to trace BEC wire transfers and leverage the FBI 72-hour Financial Fraud Kill Chain to recover stolen corporate funds rapidly.
NY DFS $250K Fine: Audit Log Lessons for Financial Institutions
Learn key audit log lessons from the recent $250K NY DFS cybersecurity settlement under 23 NYCRR Part 500 to protect your financial institution.
Anthropic AI Code Audits: Forensic Team Guide
Understand Anthropic's default AI code audit updates for Claude Code. Learn key DFIR strategies to analyze AI logs and maintain chain of custody.
Detect Abused DFIR Tools: Interlock Ransomware Threat
Learn how to detect abused DFIR tools exploited by Interlock ransomware. FICS shares critical detection strategies for enterprise security teams.
INC Ransomware Steals MFA Seeds: Forensic Response Plan
INC Ransomware exploits SonicWall SMA 1000 to steal MFA seeds. Discover FICS's expert forensic response plan to mitigate credential extraction threats.